NGINX 1.30.7 and 1.31.9 fix HTTP/2 RCE CVE-2026-123007; PoC is public
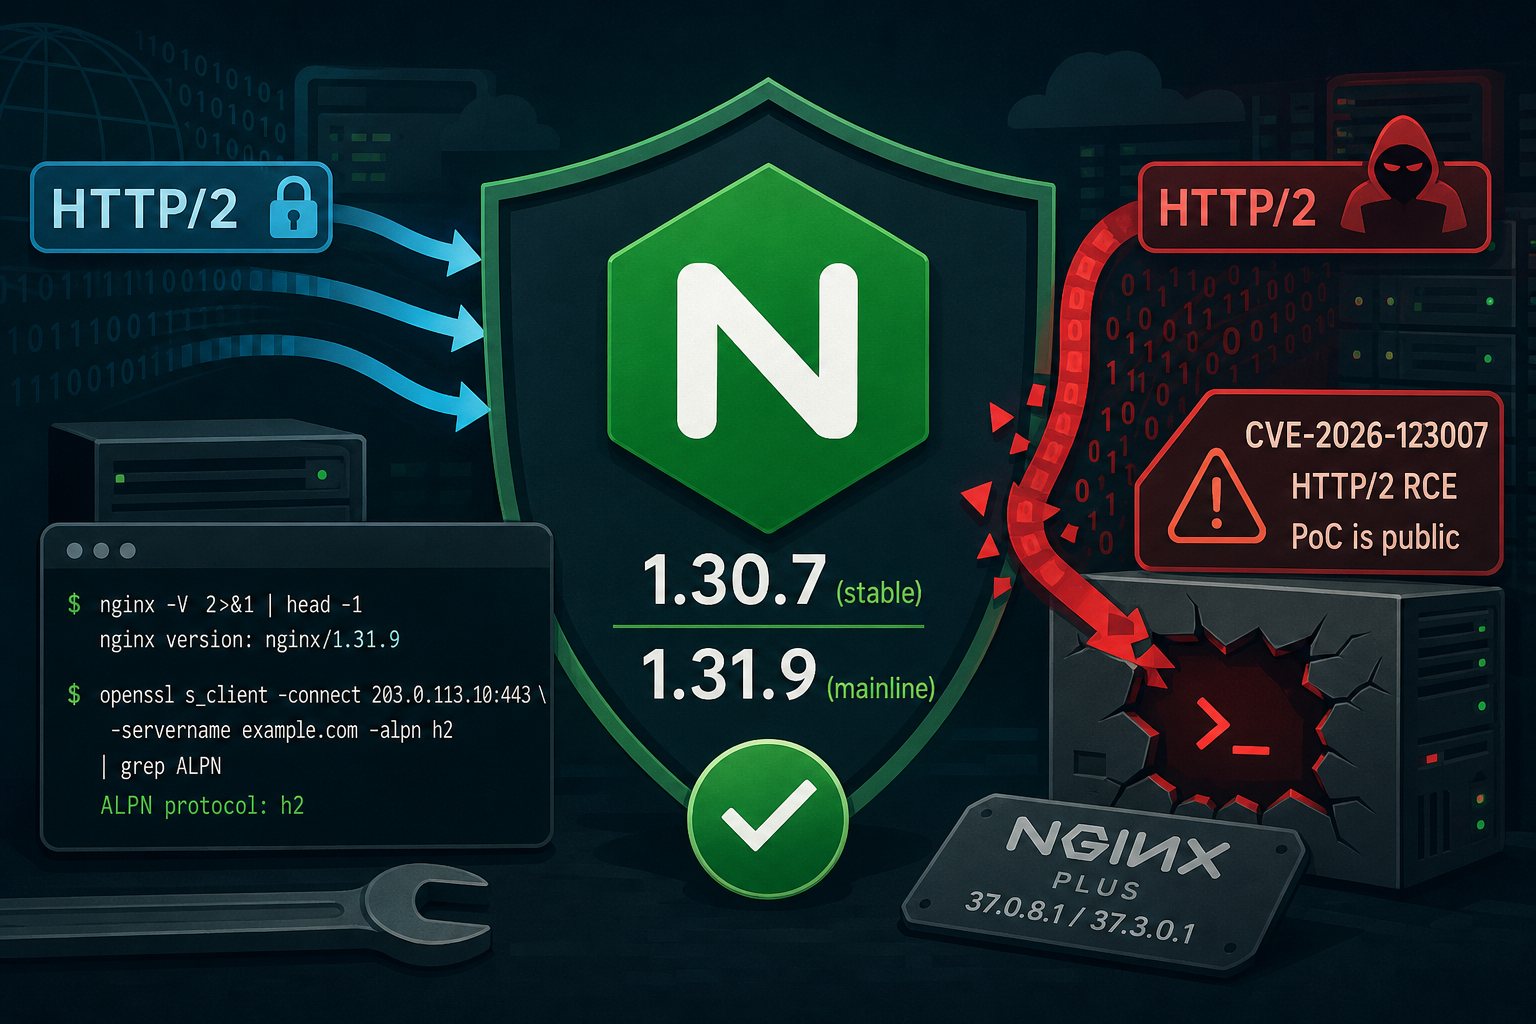
F5 released NGINX Open Source 1.30.7 (stable) and 1.31.9 (mainline) on November 18, 2026, fixing ten vulnerabilities. The most serious, CVE-2026-123007, is a memory corruption bug in HTTP/2 flow control that lets an unauthenticated attacker run code inside an NGINX worker process. It affects every release from 1.9.5, shipped in September 2015, through 1.31.8. Rapid7 published a working proof-of-concept on GitHub the same day. As of November 18 nobody had reported exploitation in the wild, and the CVE was not in CISA's Known Exploited Vulnerabilities catalog.
F5 scores five of the ten flaws at 9.2
Researchers at Xint (Theori) found the main group on October 11 and reported it to F5 through HackerOne on October 16. Wiz Research found CVE-2026-123007 and CVE-2026-123633 independently, and Rapid7 also reported CVE-2026-123007. Xint calls the set NGINX2Root. Those five carry a CVSS 4.0 score of 9.2 from F5. The nginx.org advisory rates CVE-2026-123007 "major", and Red Hat and Ubuntu score it 8.1 under CVSS 3.1, with high attack complexity.
Each of the five needs a specific feature turned on:
- CVE-2026-123007: HTTP/2 enabled. Wiz confirmed code execution on a static-only server with no third-party modules.
- CVE-2026-123633: HTTP/2 with requests proxied to an upstream, triggered when a worker runs low on free connection slots. Versions 1.19.7 through 1.31.8.
- CVE-2026-123634: a
resolverwith aproxy_passtarget built from request variables, plus amirroror SSI subrequest that looks up the same name. - CVE-2026-121810: HTTP/3 (QUIC) listeners, versions 1.25.0 and later.
- CVE-2026-113425: NGINX running as a mail proxy with
auth_http.
On a typical web hosting server, CVE-2026-123007 is the one to plan around. HTTP/2 over TLS is a standard setting on production NGINX sites, including NGINX reverse proxies in front of Apache.
The public exploit needs about 128 GB of traffic
The Rapid7 proof-of-concept (sfewer-r7/CVE-2026-123007) contains a crash trigger and a full code execution chain, demonstrated against 1.31.8 in Docker. It targets x86-64, has to defeat ASLR, and pushes roughly 128 GB of HTTP/2 traffic through one connection. Rapid7's demo took two and a half minutes. On links slower than about 300 Mbit/s the attack hits NGINX's default one-hour connection lifetime and fails, and a CDN or load balancer that terminates HTTP/2 in front of the origin makes it harder.
Xint says it ran commands against test servers at AWS, Google Cloud and Azure using only a reachable HTTP/2 port, and Wiz has working exploits it has chosen not to release.
Worker access becomes root through an unpatched SCTP kernel bug
A successful attack runs code as the NGINX worker user, usually www-data or nginx. Xint chained it with a separate use-after-free in the Linux kernel's SCTP send path, present since kernel 4.15 in 2018, to reach root, including from inside a Docker container. That kernel bug had no CVE and no fix as of November 18.
Distribution packages lag the upstream release
Most servers run distribution packages (1.24.0 on Ubuntu 24.04, 1.22.1 on Debian 12). Fixes arrive as backports, so nginx -v can report an old number on a patched build. Compare the full package version against the distribution advisory.
- Debian: the security tracker listed bookworm, trixie and forky as vulnerable on November 19. Only sid had a fixed package.
- Red Hat: rates the bug Critical and points to bulletin RHSB-2026-019. Its CVE page listed no errata yet.
- Ubuntu: fixed packages were reported on November 19 under USN-9159-1. Confirm the version for your release on ubuntu.com before marking a server done.
- NGINX Plus: fixed in 37.0.8.1 and 37.3.0.1. F5 lists no fix for the older R-series releases, so those customers need to move to 37.x.
- Control panels that bundle their own NGINX build release fixes on their own schedule. Check the vendor changelog.
Checking exposure and patching
Find the running version, the package version, and any HTTP/2 or HTTP/3 directives:
nginx -V 2>&1 | head -1
dpkg -l nginx          # Debian/Ubuntu
rpm -q nginx           # RHEL/AlmaLinux
grep -rnE 'http2|quic|http3' /etc/nginx/
Test from outside. If the site sits behind a CDN, connect to the origin IP directly, because the origin is the target:
echo | openssl s_client -connect 203.0.113.10:443 \
  -servername example.com -alpn h2 2>/dev/null | grep ALPN
ALPN protocol: h2 means HTTP/2 is reachable. Once a fixed package is available, install it and restart:
apt update && apt install --only-upgrade nginx   # Debian/Ubuntu
dnf upgrade nginx                                  # RHEL/AlmaLinux
systemctl restart nginx
Use restart, not reload. A reload re-reads the configuration but leaves the old executable running. Confirm the master process start time is after the upgrade with ps -o lstart= -p $(cat /run/nginx.pid). On the servers we manage, that check is part of every NGINX update.
Temporary mitigations while waiting on a package
Turning off HTTP/2 blocks CVE-2026-123007 and CVE-2026-123633. On NGINX 1.25.1 and later, set http2 off; in each affected server block and remove http2 from listen lines. On older versions, change listen 443 ssl http2; to listen 443 ssl;. The listen parameter applies to every virtual host sharing that address and port, so one missed server block leaves HTTP/2 on for all of them. Run nginx -t, reload, and repeat the openssl test until ALPN protocol: h2 no longer appears.
Remove QUIC listeners and any Alt-Svc header if you run HTTP/3. Bind mail proxy listeners to loopback or firewall them. On hosts that do not use SCTP, block the module:
echo 'install sctp /bin/false' > /etc/modprobe.d/disable-sctp.conf
lsmod | grep sctp
That stops future loads only. If lsmod shows it loaded, unload it with modprobe -r sctp or reboot. It has no effect on kernels with SCTP built in.
Log entries and process behavior that point to an attempt
HTTP/2 control frames do not appear in access logs, so a clean access log proves little. Look for workers dying in the error log:
grep 'exited on signal' /var/log/nginx/error.log*Other signs CIRCL and Xint list: core dumps from NGINX, long-lived HTTP/2 connections with heavy inbound traffic and few logged requests, worker processes starting shells or other programs, and unexpected outbound connections or DNS lookups from the web server.