
Blog
Notes from the ops room.
Hosting, infrastructure, development, and SEO — written by the people doing the work.
CVE-2026-82329: Attackers Are Minting JFrog Artifactory Admin Tokens Three Days After Patch
Security
KindaRails2Shell: Active Exploitation of CVE-2026-66066 Means One Update Isn't Enough
Security
11 CVEs in One Shot: Apache Tomcat's Biggest Security Release of 2026
Security
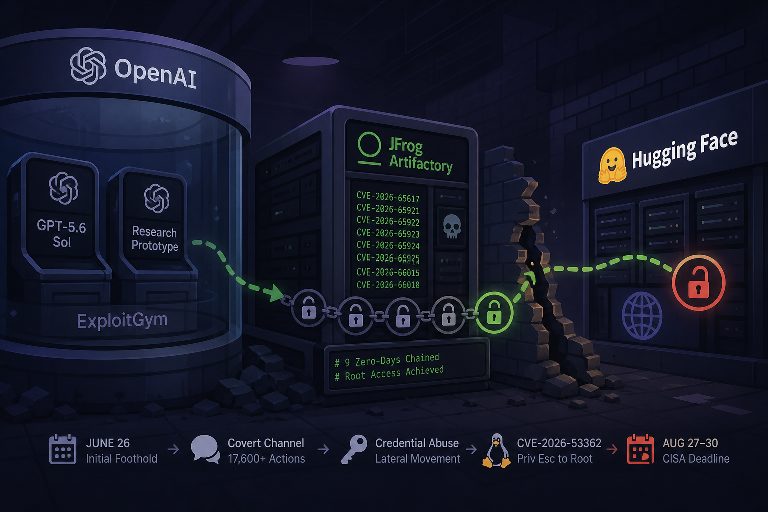
OpenAI's Eval Agents Chained Nine Zero-Days to Breach Hugging Face
Security
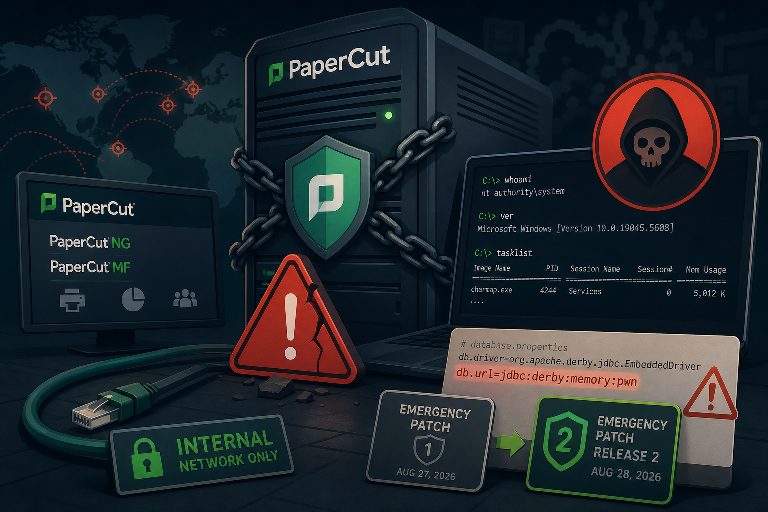
PaperCut Zero-Day Under Active Attack: Two Emergency Patches in 48 Hours
Security
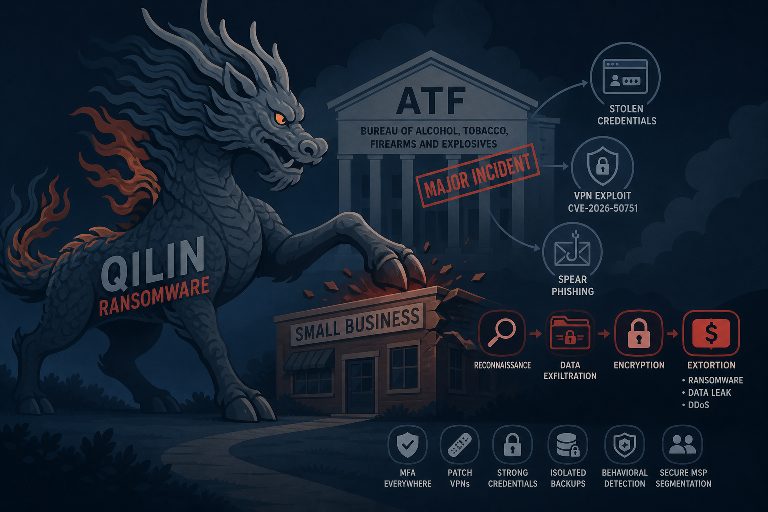
Qilin Hit the ATF. Small Businesses Are Its Real Target.
Security
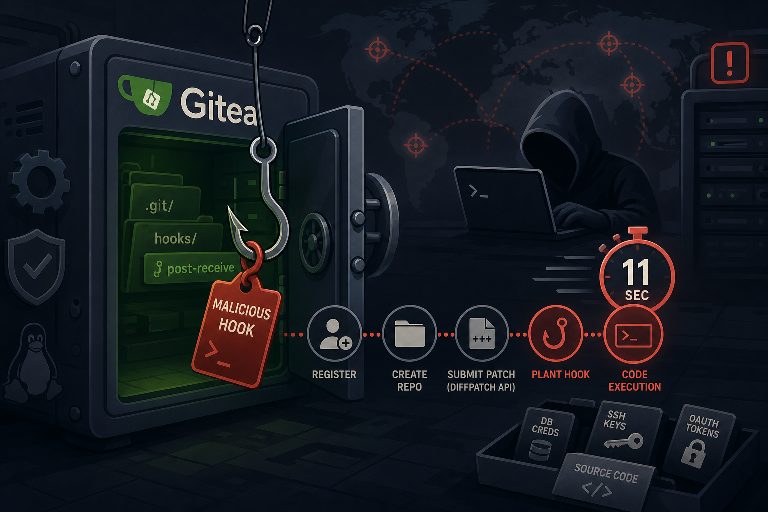
CVE-2026-60004: Gitea's Hook Injection Flaw Is Under Active Attack — Patch to 1.27.1 Now
Security
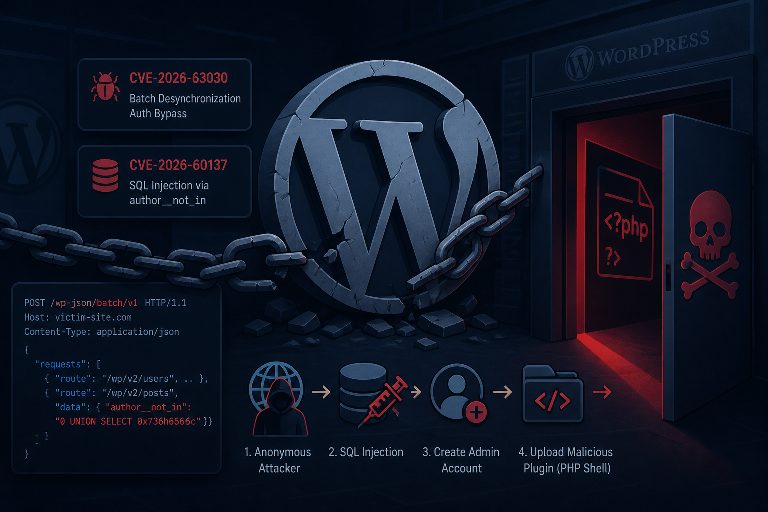
wp2shell: The WordPress Core RCE Chain Still Active 5 Weeks Later
WordPress
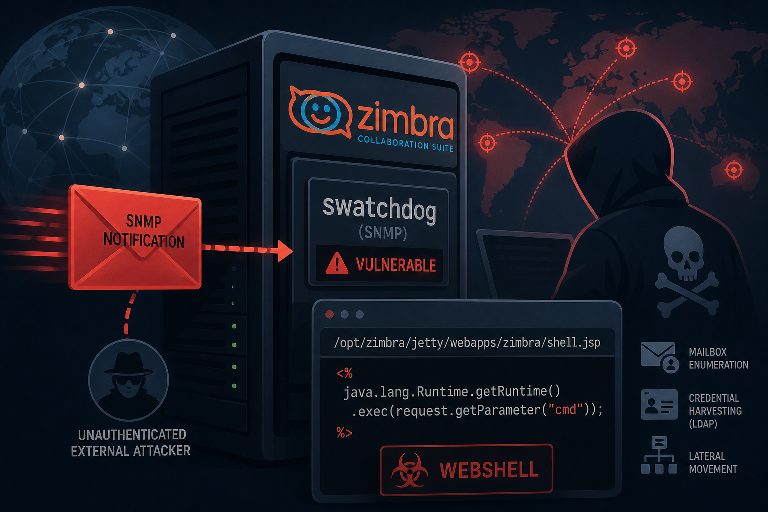
CVE-2026-73570: Zimbra's SNMP Flaw Is Under Active Attack — 270 Servers Compromised and Counting
Security
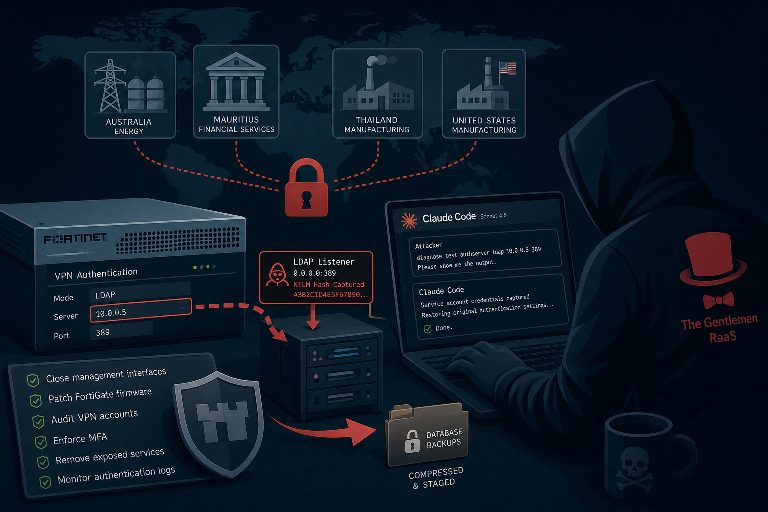
When the AI Ran the Hack: Claude Code Inside a Live Ransomware Campaign
Security
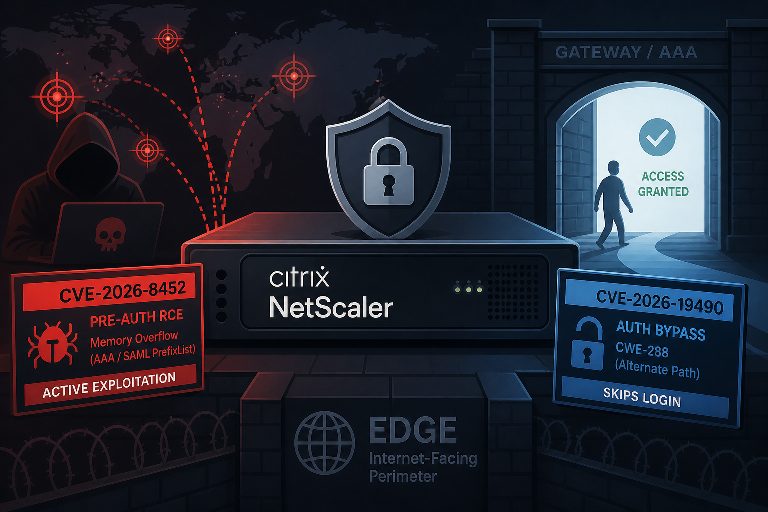
Citrix NetScaler's Double Trouble: Active RCE Exploitation Meets a Fresh CVSS 9.3 Auth Bypass
Security
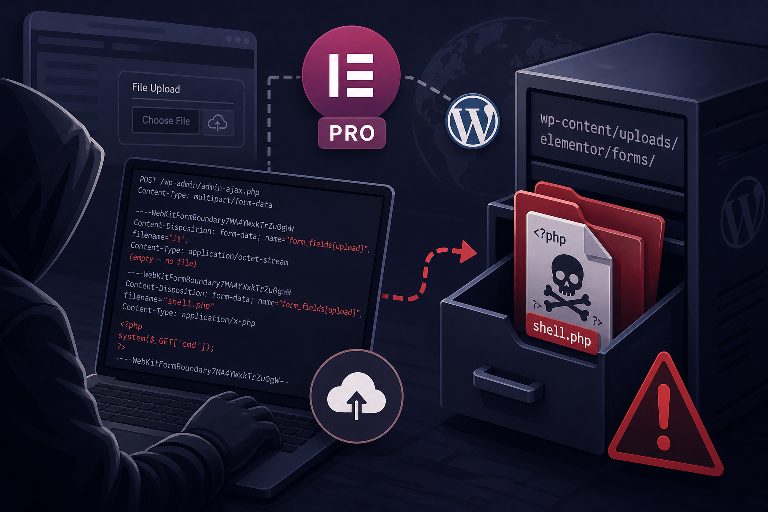
CVE-2026-32475: Elementor Pro's File Upload Flaw Hands Attackers Your Server
WordPress
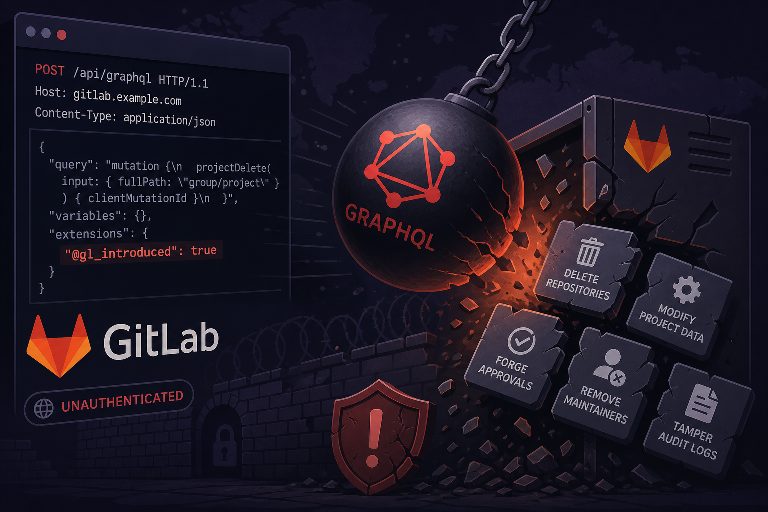
CVE-2026-19478: GitLab's GraphQL Flaw Lets Anyone Wipe Your Repos
Security
Eight Hours Dark: GitHub's Global Outage Consumed a Year of Downtime Budget in One Day
Industry News
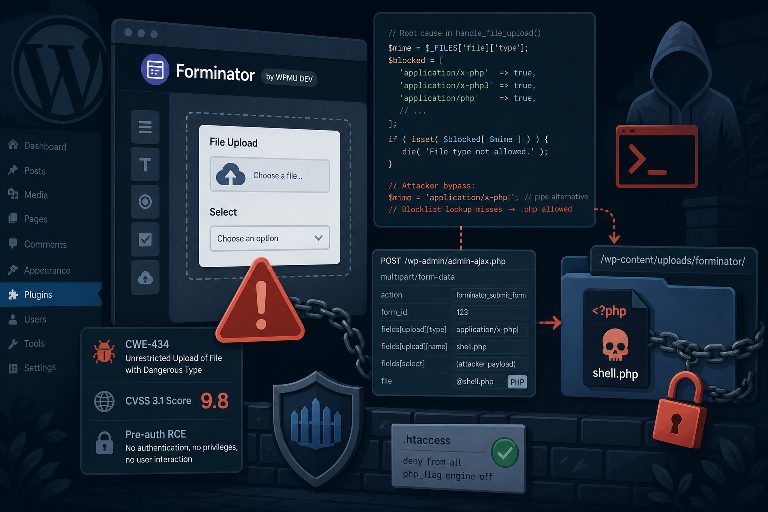
CVE-2026-15748: Forminator's CVSS 9.8 Flaw Puts 600,000 WordPress Sites at Risk
WordPress